Updated SC-100 Dumps Questions Are Available [2026] For Passing Microsoft Exam [Q10-Q33]

4/5 - (1 vote)

Updated SC-100 Dumps Questions Are Available [2026] For Passing Microsoft Exam

Free UPDATED Microsoft SC-100 Certification Exam Dumps is Online

To prepare for the Microsoft SC-100 certification exam, you’ll need to have a solid understanding of cybersecurity fundamentals and a strong foundation in computer networking and architecture. You can also take advantage of Microsoft’s online training resources and study guides to help you prepare for the exam. Microsoft also offers a range of practice tests and simulations to help you familiarize yourself with the exam format and identify areas where you may need to focus your study efforts.

Microsoft SC-100 (Microsoft Cybersecurity Architect) Certification Exam is an important certification for cybersecurity professionals who wish to demonstrate their expertise in securing Microsoft technologies and protecting against today’s sophisticated cyber threats. SC-100 exam covers a range of topics, including security concepts, threat management, identity, access management, platform protection, data and application protection, and governance, risk management, and compliance. Candidates who pass the exam will demonstrate the skills and knowledge required to design and implement secure solutions using Microsoft technologies.


Q10. You have a Microsoft 365 subscription
You need to recommend a security solution to monitor the following activities:
* User accounts that were potentially compromised
* Users performing bulk file downloads from Microsoft SharePoint Online What should you include in the recommendation for each activity? To answer, drag the appropriate components to the correct activities. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each Correct selection is worth one Point.

Q11. Case Study 1 – Fabrikam, Inc
OverView
Fabrikam, Inc. is an insurance company that has a main office in New York and a branch office in Paris.
Existing Environment
On-premises Environment
The on-premises network contains a single Active Directory Domain Services (AD DS) domain named corp.fabrikam.com.
Azure Environment
Fabrikam has the following Azure resources:
– A Microsoft Entra tenant named fabrikam.onmicrosoft.com that syncs with corp.fabrikam.com
– A single Azure subscription named Sub1
– A virtual network named Vnet1 in the East US Azure region
– A virtual network named Vnet2 in the West Europe Azure region
– An instance of Azure Front Door named FD1 that has Azure Web Application Firewall (WAF) enabled
– A Microsoft Sentinel workspace
– An Azure SQL database named ClaimsDB that contains a table named ClaimDetails
– 20 virtual machines that are configured as application servers and are NOT onboarded to Microsoft Defender for Cloud
– A resource group named TestRG that is used for testing purposes only
– An Azure Virtual Desktop host pool that contains personal assigned session hosts
– All the resources in Sub1 are in either the East US or the West Europe region.
Partners
Fabrikam has contracted a company named Contoso, Ltd. to develop applications. Contoso has the following infrastructure:
– An Microsoft Entra named contoso.onmicrosoft.com
– An Amazon Web Services (AWS) implementation named ContosoAWS1 that contains AWS EC2 instances used to host test workloads for the applications of Fabrikam Developers at Contoso will connect to the resources of Fabrikam to test or update applications.
The developers will be added to a security Group named Contoso Developers in fabrikam.onmicrosoft.com that will be assigned to roles in Sub1. The ContosoDevelopers group is assigned the db.owner role for the ClaimsDB database.
Compliance Event
Fabrikam deploys the following compliance environment:
– Defender for Cloud is configured to assess all the resources in Sub1 for compliance to the HIPAA HITRUST standard.
– Currently, resources that are noncompliant with the HIPAA HITRUST standard are remediated manually.
– Qualys is used as the standard vulnerability assessment tool for servers.
Problem Statements
The secure score in Defender for Cloud shows that all the virtual machines generate the following recommendation. Machines should have a vulnerability assessment solution. All the virtual machines must be compliant in Defender for Cloud.
ClaimApp Deployment
Fabrikam plans to implement an internet-accessible application named ClaimsApp that will have the following specification
– ClaimsApp will be deployed to Azure App Service instances that connect to Vnet1 and Vnet2.
– Users will connect to ClaimsApp by using a URL of https://claims.fabrikam.com.
– ClaimsApp will access data in ClaimsDB.
– ClaimsDB must be accessible only from Azure virtual networks.
– The app services permission for ClaimsApp must be assigned to ClaimsDB.
Application Development Requirements
Fabrikam identifies the following requirements for application development:
– Azure DevTest labs will be used by developers for testing.
– All the application code must be stored in GitHub Enterprise.
– Azure Pipelines will be used to manage application deployments.
– All application code changes must be scanned for security vulnerabilities, including application code or configuration files that contain secrets in clear text. Scanning must be done at the time the code is pushed to a repository.
Security Requirement
Fabrikam identifies the following security requirements:
– Internet-accessible applications must prevent connections that originate in North Korea.
– Only members of a group named InfraSec must be allowed to configure network security groups (NSGs} and instances of Azure Firewall, VJM. And Front Door in Sub1.
– Administrators must connect to a secure host to perform any remote administration of the virtual machines. The secure host must be provisioned from a custom operating system image.
AWS Requirements
Fabrikam identifies the following security requirements for the data hosted in ContosoAWSV.
– Notify security administrators at Fabrikam if any AWS EC2 instances are noncompliant with secure score recommendations.
– Ensure that the security administrators can query AWS service logs directly from the Azure environment.
Contoso Developer Requirements
Fabrikam identifies the following requirements for the Contoso developers:
– Every month, the membership of the ContosoDevelopers group must be verified.
– The Contoso developers must use their existing contoso.onmicrosoft.com credentials to access the resources in Sub1.
– The Comoro developers must be prevented from viewing the data in a column named MedicalHistory in the ClaimDetails table.
Compliance Requirement
Fabrikam wants to automatically remediate the virtual machines in Sub1 to be compliant with the HIPPA HITRUST standard. The virtual machines in TestRG must be excluded from the compliance assessment.
Hotspot Question
You are evaluating the security of ClaimsApp.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Q12. You need to recommend a multi-tenant and hybrid security solution that meets to the business requirements and the hybrid requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

Q13. A customer uses Azure to develop a mobile app that will be consumed by external users as shown in the following exhibit.

You need to design an identity strategy for the app. The solution must meet the following requirements:
* Enable the usage of external IDs such as Google, Facebook, and Microsoft accounts.
* Be managed separately from the identity store of the customer.
* Support fully customizable branding for each app.
Which service should you recommend to complete the design?


Q14. You need to recommend a solution to meet the compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q15. Your company is migrating data to Azure. The data contains Personally Identifiable Information (Pll). The company plans to use Microsoft Information Protection for the Pll data store in Azure. You need to recommend a solution to discover Pll data at risk in the Azure resources.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q16. Hotspot Question
You plan to deploy an Azure API Management solution that will enable different groups of developers to access different sets of APIs at random times and rates.
You need to recommend the pricing tier that should be purchased and the scope at which the rate limit policies should be applied. The solution must meet the following requirements:
– Ensure that each group of developers can access only specific sets of APIs.
– Ensure that each set of APIs can be configured with specific rate
limits.
– Minimize development and administrative effort and costs.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q17. Your company finalizes the adoption of Azure and is implementing Microsoft Defender for Cloud.
You receive the following recommendations in Defender for Cloud:
– Access to storage accounts with firewall and virtual network
configurations should be restricted
– Storage accounts should restrict network access using virtual network rules.
– Storage account should use a private link connection.
– Storage account public access should be disallowed.
You need to recommend a service to mitigate identified risks that relate to the recommendations.
What should you recommend?


Q18. You need to recommend a strategy for App Service web app connectivity. The solution must meet the landing zone requirements. What should you recommend? To answer, select the appropriate options in the answer are a. NOTE Each correct selection is worth one point.

Q19. Hotspot Question
You have a multi-cloud environment that contains an Azure subscription and an Amazon Web Services (AWS) account.
You need to implement security services in Azure to manage the resources in both subscriptions.
The solution must meet the following requirements:
– Automatically identify threats found in AWS CloudTrail events.
– Enforce security settings on AWS virtual machines by using Azure
policies.
What should you include in the solution for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q20. You are designing security for a runbook in an Azure Automation account. The runbook will copy data to Azure Data Lake Storage Gen2.
You need to recommend a solution to secure the components of the copy process.
What should you include in the recommendation for each component? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

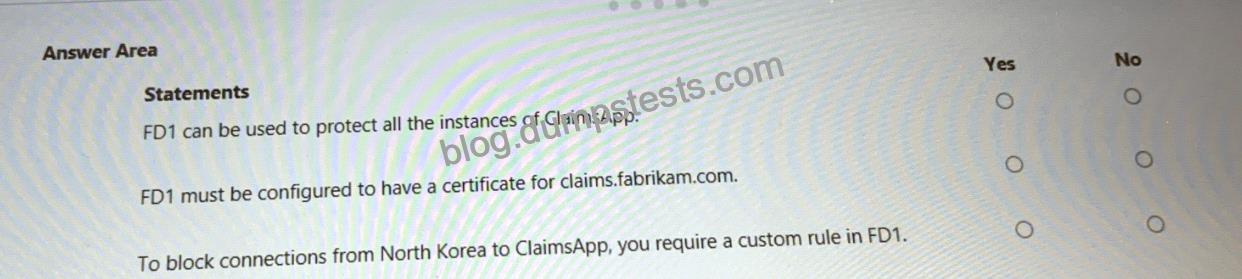
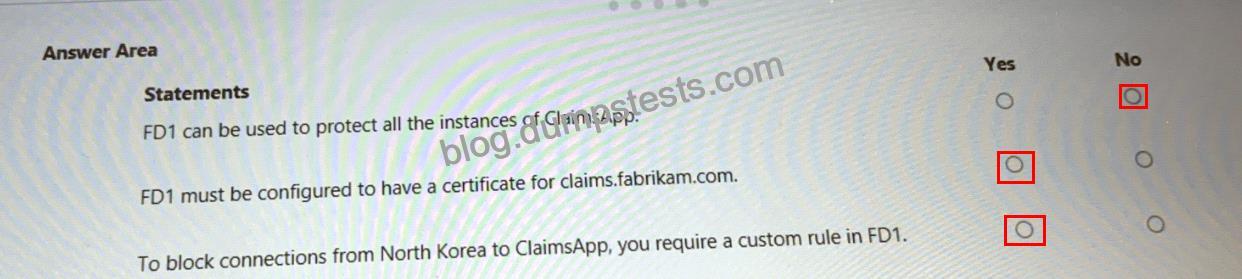
Q21. You are evaluating the security of ClaimsApp.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE; Each correct selection is worth one point.
Q22. You are designing security for a runbook in an Azure Automation account. The runbook will copy data to Azure Data Lake Storage Gen2.
You need to recommend a solution to secure the components of the copy process.
What should you include in the recommendation for each component? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

Q23. Your company has a Microsoft 365 E5 subscription, an Azure subscription, on-premises applications, and Active Directory Domain Services (AD DSV You need to recommend an identity security strategy that meets the following requirements:
* Ensures that customers can use their Facebook credentials to authenticate to an Azure App Service website
* Ensures that partner companies can access Microsoft SharePoint Online sites for the project to which they are assigned The solution must minimize the need to deploy additional infrastructure components. What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q24. You are creating the security recommendations for an Azure App Service web app named App1.
App1 has the following specifications:
* Users will request access to App1 through the My Apps portal. A human resources manager will approve the requests.
* Users will authenticate by using Azure Active Directory (Azure AD) user accounts.
You need to recommend an access security architecture for App1.
What should you include in the recommendation? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.

Q25. You have a Microsoft 365 subscription and an Azure subscription. Microsoft 365 Defender and Microsoft Defender for Cloud are enabled.
The Azure subscription contains a Microsoft Sentinel workspace. Microsoft Sentinel data connectors are configured for Microsoft 365, Microsoft 365 Defender, Defender for Cloud, and Azure.
You plan to deploy Azure virtual machines that will run Windows Server.
You need to enable extended detection and response (EDR) and security orchestration, automation, and response (SOAR) capabilities for Microsoft Sentinel.
How should you recommend enabling each capability? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q26. You have two Azure subscriptions named Sub1 and Sub2 that contain the vaults shown in the following table.

You need to design a multi-user authorization (MUA) solution for security operations on the vaults. The solution must meet the following requirements:
– RSVault1 and RSVault2 must require MUA for disabling soft delete,
removing MUA protection, and disabling immutability.
– BackupVault1 and BackupVault2 must require MUA for disabling soft
delete and removing MUA protection.
What is the minimum number of Resource Guard resources required?


Q27. You need to recommend a solution to meet the requirements for connections to ClaimsDB.
What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q28. Your company has a third-party security information and event management (SIEM) solution that uses Splunk and Microsoft Sentinel. You plan to integrate Microsoft Sentinel with Splunk.
You need to recommend a solution to send security events from Microsoft Sentinel to Splunk. What should you include in the recommendation?


Q29. You need to recommend a solution to meet the security requirements for the InfraSec group. What should you use to delegate the access?


Q30. Hotspot Question
You plan to automate the development and deployment of a Node.js-based app by using GitHub.
You need to recommend a DevSecOps solution for the app. The solution must meet the following requirements:
– Automate the generation of pull requests that remediate identified
vulnerabilities.
– Automate vulnerability code scanning for public and private
repositories.
– Minimize administrative effort.
– Minimize costs.
What should you recommend using? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q31. You need to recommend a SIEM and SOAR strategy that meets the hybrid requirements, the Microsoft Sentinel requirements, and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q32. Drag and Drop Question
You have a hybrid Azure AD tenant that has pass-through authentication enabled.
You are designing an identity security strategy.
You need to minimize the impact of brute force password attacks and leaked credentials of hybrid identities.
What should you include in the design? To answer, drag the appropriate features to the correct requirements. Each feature may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

Q33. You need to recommend a solution to evaluate regulatory compliance across the entire managed environment. The solution must meet the regulatory compliance requirements and the business requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.


Microsoft Exam 2026 SC-100 Dumps Updated Questions: https://www.dumpstests.com/SC-100-latest-test-dumps.html

Related Links: myportal.utt.edu.tt myportal.utt.edu.tt learn.csisafety.com.au myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt

No Responses

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below
 

Recent Comments